After installing my new pfSense firewall, I wanted to expose some of my servers to the internet. First, I had HTTP and HTTPS made available for this blog by using NAT. But that’s not very secure, so I found HAProxy, a module inside pfSense. It’s a reverse proxy, among other things.
I configured it to use ACME, another module inside pfSense, to acquire SSL certificates from Let’s Encrypt, handle all SSL traffic and then send the requests to my internal servers. The internal servers no longer need to handle SSL traffic, so they talk to the HAProxy with unencrypted port 80 traffic. Thus separating the outside WAN from my servers on the inside LAN. I found an excellent guide on how to set this up.
Problem with internal access
But I could not get calls to the servers from the internal network to work properly. So I decided to route all internal calls on LAN to the HAProxy as well. But it refused to work. I did Host Overrides so that the URL of the servers pointed to my pfSense firewall. I configured HAProxy to listen to the LAN network as well as WAN, but that didn’t fix it. But after hours of searching, I found the solution.
Solution
Inside the HAProxy settings, under Front End, I configured it to listen to LAN as well as WAN. Because that feels obvious, doesn’t it?
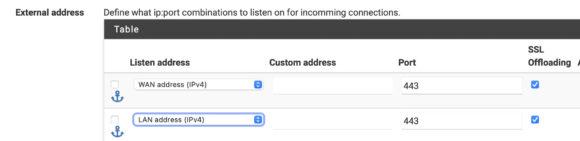
But no. That doesn’t work. You need to set it to Any (IPv4) instead of LAN Address (IPv4).
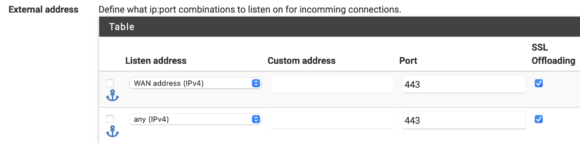
Now I can access all the servers on the inside with SSL encryption, and an added bonus to be able to access different servers on port 443 from WAN and LAN by using rules on HAProxy just by using different subdomains. Very nifty. Hopefully you landed on this page if you had the same problem.
Don’t forget to setup a new rule on your firewall to allow LAN traffic to port 443 on your pfSense firewall. And naturally you need to change your access port to the pfSense firewall to something else than 443 to avoid conflict.
Any chance you can elaborate on your firewall rules or HAProxy setup to make this work? Do you still have to DNS resolve each individual host name to your firewall to get it picked up by the reverse proxy?
This seems like my exact setup but im struggling to get this working.
Same problem for me cannot get it working from LAN.
same here, my domain is pointing to my static IP address, I have port forwarding from my Internet modem to the PfSense on 80 and 443 my pfsense wan address is 10.0.0.10 my server is 192.168.1.10 working fine from the internet, but when I try from my internal network(192 or10) I get the timeout.
same here, my domain is pointing to my static IP address, I have port forwarding from my Internet modem to the PfSense on 80 and 443 my pfsense wan address is 10.0.0.10 my server is 192.168.1.10 working fine from the internet, but when I try from my internal network(192 or10) I get the timeout.
Did you look into nat reflection/hairpin? https://docs.netgate.com/pfsense/en/latest/nat/reflection.html “ NAT reflection refers to the ability to access external services from the internal network using the external (usually public) IP address, the same as if the client were on the Internet.”
Does not matter. There is a mistake. The "Lever-shifter" as designed on board cannot work! Yes, schematic is OK, but then there is a short connection between transistors pins 2 and 3 as he put the same name "SDA_3V" on both its sides . Jack wrote he will fix it during the weekend but hi did not. (he did not specified what a weekend in year :-) ) I can send you corrected board (a bit different design I use only 3 outputs and 1 ext clock input)
sorry I wrote comment to wrong thread :-)